Undercover Agent
Mission-Critical Technology
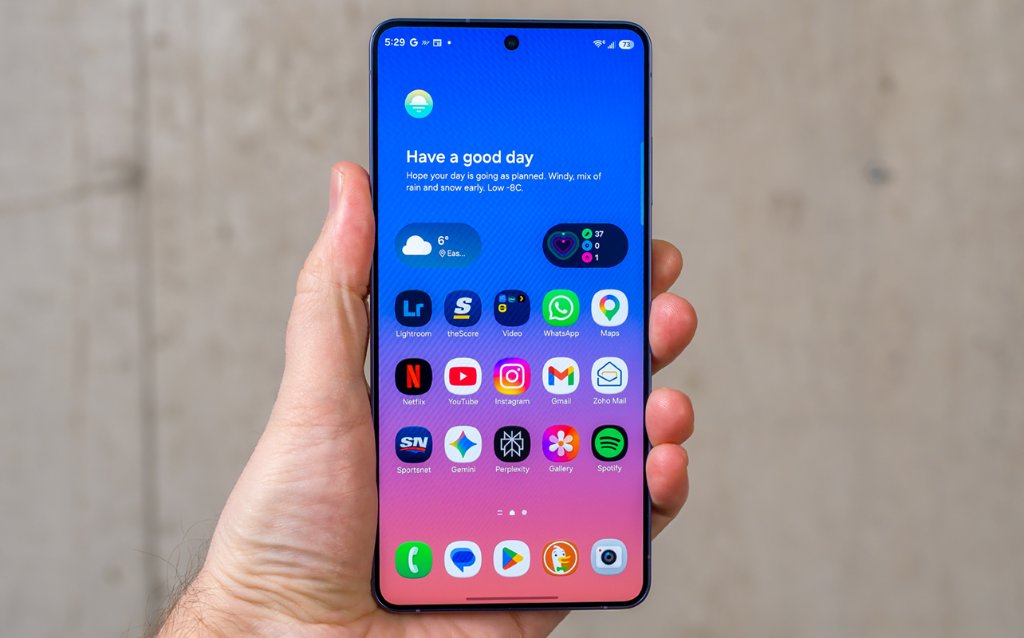
Cyber Intelligence Gathering Platform for Undercover Agents, built to run on the Android smartphones carried by undercover operatives, infiltrated agents and field intelligence personnel — connected to a Command & Control dashboard operated exclusively by your agency.
Complete Source Code
Full source code, blueprints and engineering documentation delivered to your agency.
On-Premise Deployment
Installed on your own servers and secure infrastructure — no external cloud dependency.
Independent Audit
Your technical team inspects and audits every delivered line of code.
Training & Support
Technical support, installation assistance and operator training included.
Purpose-built for covert field operations
Our platform enables authorized command centers to securely monitor, communicate with, protect and coordinate undercover agents operating inside criminal organizations, organized crime networks, drug trafficking groups, terrorist organizations and other high-risk environments.
Monitor
Oversight of every enrolled operative device from one agency-controlled dashboard, with lawful collection of device and communications intelligence.
Communicate
Encrypted tasking, instructions and intelligence exchange between command centers and operatives in the field.
Protect
Live location awareness, emergency alerts and rapid-response coordination when an operative's cover is at risk.
Coordinate
Operational coordination across teams and missions, with every piece of intelligence tied to the authorized case file.
Each authorized agent's Android smartphone runs our dedicated application and connects the field operative to a centralized Command & Control (C2) dashboard — operated exclusively by the acquiring agency.
One platform, four operational layers
Everything an authorized command center needs to run and safeguard an undercover operation — from device collection to AI analysis, agent protection and encrypted communications.
Undercover Agent Smartphone Monitoring
Centralized monitoring and remote operational oversight of all enrolled Android devices through the C2 dashboard.
- GPS location tracking and operational movement history
- Authorized call recording — cellular and VoIP, including WhatsApp, Telegram and Signal
- Text messaging across all platforms and social media, SMS and call log collection
- Nearby Wi-Fi networks, contacts, accounts, emails and calendar
- Front and rear camera access, microphone recordings of the environment and screen recording
- File system data, installed applications and full device inventory
AI-Powered Operational Intelligence
AI assistance turns raw device collection into actionable field intelligence for the case team.
- AI-assisted analysis of intelligence collected from authorized devices
- Transcription and translation of operational audio
- Intelligence correlation, automated summaries and investigative reporting
- Identification of potential operational risks and relevant intelligence patterns
Agentic SOC
AI agents gather information, cross-reference intelligence, investigate events, prioritize alerts and trigger controlled automation processes — for smarter detection and investigation.
Undercover Agent Protection & Coordination
Command keeps continuous awareness of the operative, not just the device.
- Real-time location awareness for authorized command personnel
- Emergency alerts and rapid-response coordination
- Improved situational awareness during infiltration operations
- Secure communication between undercover operatives and their command centers
Secure Communications & Evidence Protection
Cyber-Link and CryptShield protect the operation itself — orders, intelligence and evidence.
- Highly encrypted communications through our Cyber-Link technology
- Confidential exchange of operational instructions, messages and sensitive intelligence
- Quantum-resistant encryption through CryptShield
- Protection of sensitive operational documents, intelligence files and digital evidence
Mission-critical technology for operations and investigations
The Implant on the infiltrated agent phone delivers critical covert communication capabilities for federal agents conducting complex investigations across jurisdictions. Every incoming and outgoing call on every platform — cellular, WhatsApp, Telegram, Signal and other messengers — is recorded and accessible on the C2 platform, so task forces gather court-admissible evidence that stays securely stored off-device.
The solution enables real-time monitoring by supervisory teams who receive immediate alerts when communications occur, allowing them to listen in on calls and review text messages while tracking the precise location of undercover personnel and confidential human sources.
Every call recorded, on every platform
All incoming and outgoing calls — cellular, WhatsApp, Telegram, Signal and other messengers — are recorded and accessible on the C2 platform.
SMS and every message, on every platform
Any SMS and any message received on the agent phone — WhatsApp, Telegram, Signal, Facebook and other messengers — is accessible on the C2 platform, including the images, videos and voice messages sent with it.
Room audio, even on standby
The infiltrated agent's phone, fully controlled by the C2 platform, can record ambient room audio on demand — including while the handset is in standby mode.
Remote camera capture, even on standby
Front and rear cameras can be triggered from the C2 platform to take pictures on demand — including while the agent phone is in standby mode.
Court-admissible evidence
Not only calls — every message, room audio recording, photo, video, location log and other item of evidence collected by the agent phone is captured, hashed and stored off-device, so task forces preserve chain of custody for prosecution.
Immediate supervisor alerts
Supervisory teams are notified the moment any activity occurs — calls, messages, room audio, camera captures or a position change — then listen in on calls, review messages and retrieve new evidence in real time.
Precise location tracking
Command tracks the exact position of undercover personnel and confidential human sources while the operation moves across jurisdictions.
Incoming call · WhatsApp · +1 (202) 555-0147
Every call, every platform · cellular, WhatsApp, Telegram, Signal · recorded on C2
Audio streaming to supervisory team
Live · 02:41 elapsed
“Pickup at dock 4, 02:00.”
SMS · WhatsApp · Telegram · Signal · Facebook — media included
Ambient room audio · handset in standby
Triggered from C2 · 00:48 captured · screen off
Rear camera · 3 frames · handset in standby
Triggered from C2 · front & rear selectable
CHS-114 · 38.8977° N, 77.0365° W
Precise position · updated 3s ago
Purpose-built communication and surveillance solutions trusted by federal agencies for mission-critical operations.
The Command & Control dashboard your agency operates
A centralized C2 dashboard, operated exclusively by the acquiring agency, delivering real-time oversight of every enrolled undercover agent device — communications, location, cameras, microphone, files and operational intelligence in one workspace.
The Command and Control Dashboard
Your PC remotely controls the Samsung device through the C2 dashboard for remote surveillance and lawful interception. The Overview page delivers a single-screen technical fingerprint of the monitored device — everything you need to assess its state, exposure, and operational value.
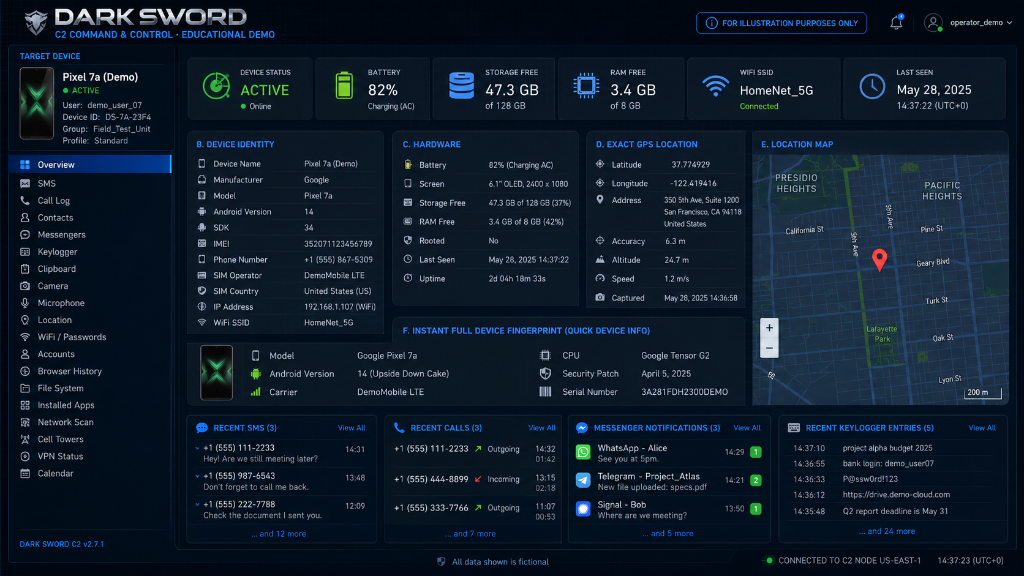
Device Telemetry Captured
Security Significance
This feature gives the operator an immediate technical fingerprint of the device. It helps identify the exact phone model, Android version, carrier, connectivity state, and whether the device is currently active.
In a threat-analysis context, this information can be used to determine the device's exposure level, possible vulnerabilities, privilege state, and operational value — all from a single consolidated view.
SMS Monitoring Page
The SMS module displays inbound and outbound messages. For each message it captures sender number, receiver number, full message content, timestamp, and direction — received or sent.
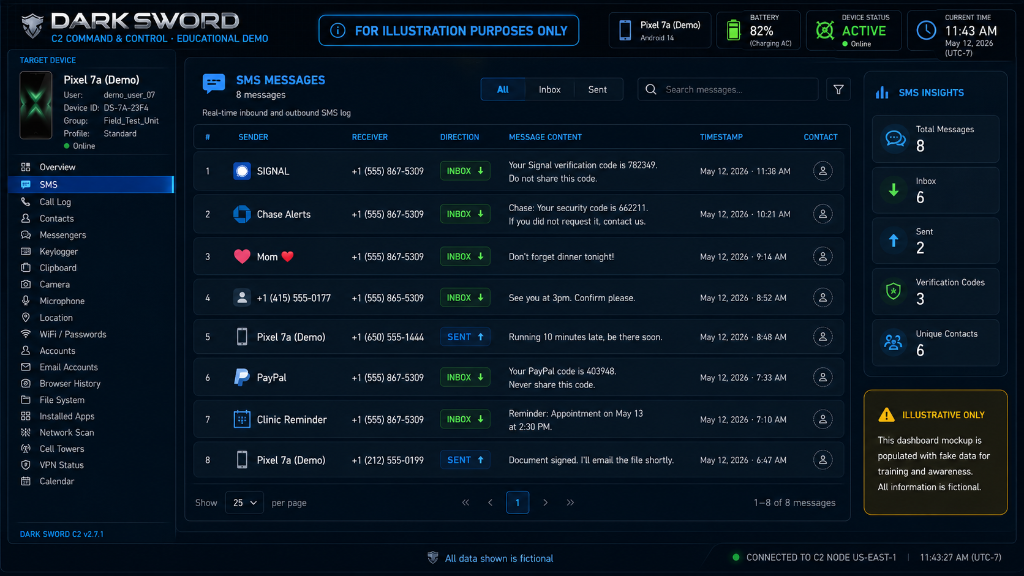
Security Significance
SMS access is highly sensitive because SMS is still widely used for one-time passwords, banking alerts, verification codes, appointment confirmations, account recovery, and private communications. Intercepting this channel provides a comprehensive view of the target's authentication activities and personal correspondence.
High-Value SMS Categories
Call Log Page
The call log module displays incoming, outgoing, missed, rejected, and unknown calls. It may include the contact name, phone number, call type, call duration, date, and exact time.
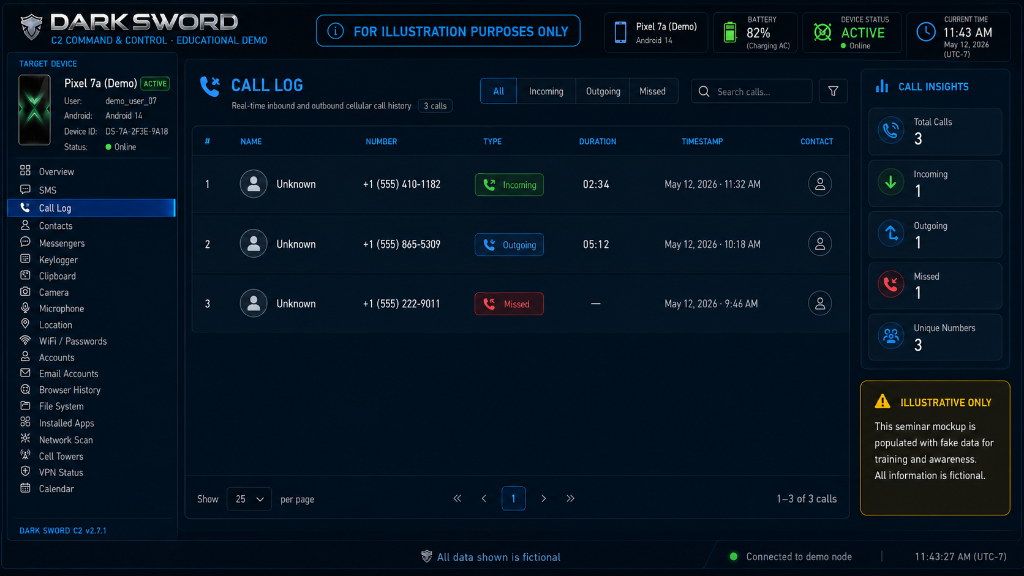
Security Significance
Call logs expose relationship patterns. Even without recording the call content, call metadata can reveal who the user communicates with, how often, and at what times. It reveals social structure, habits, and trusted relationships — including relationship mapping, business intelligence collection, and identification of lawyers, banks, doctors, family members, colleagues, and other sensitive contacts.
Intelligence Value
Call Recording Page
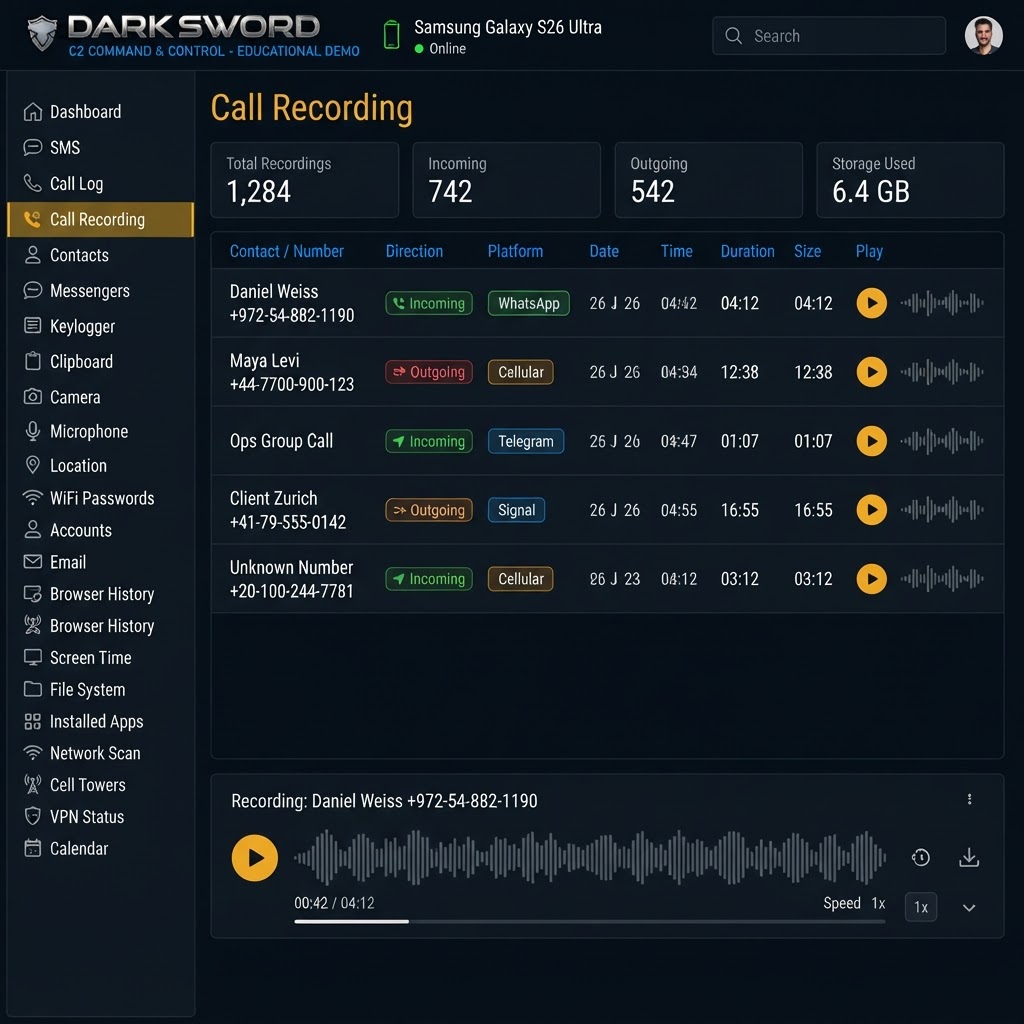
Every call on the device — cellular, WhatsApp, Telegram, and Signal — is recorded automatically, incoming or outgoing, and stored on the Call Recording page for on-demand playback, download, and long-term archive.
Automatic Capture
Recording starts the moment a call connects and stops when it ends, whichever application carries it and whichever direction it travels. Nothing has to be enabled on the device, and no notification is shown to the user.
Recording Library
Each entry carries the contact, number, direction, platform, date, time, duration, and file size — with an inline audio player for immediate review and a download option for forensic use.
Contacts Page
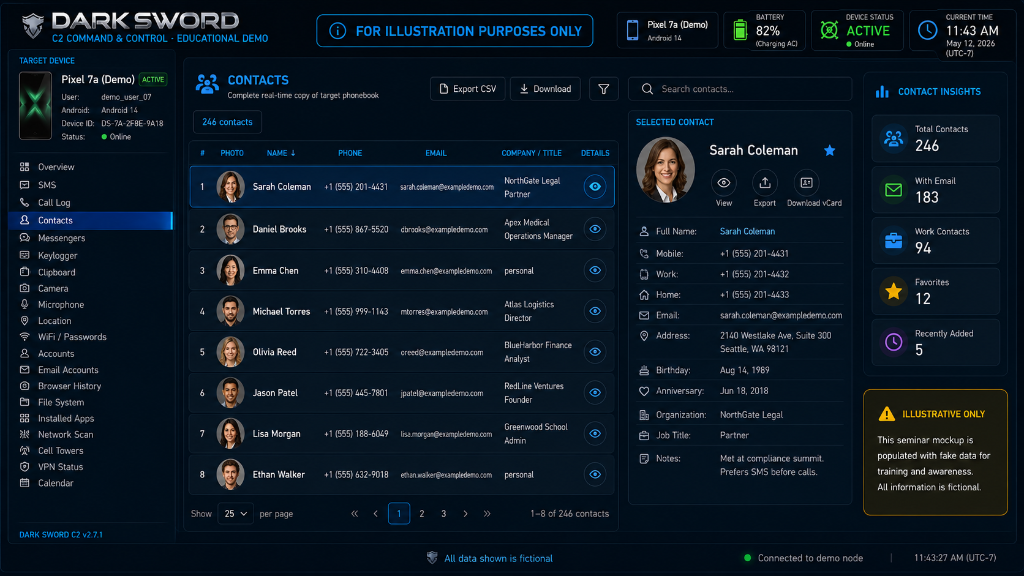
The contacts module extracts the full phonebook — names, phone numbers, email addresses, physical addresses, birthdays, notes, contact photos, organizations, and job titles. Includes search and export functions for operational use.
Security Significance
A full contact list gives the operator a ready-made map of the target's personal and professional network. Once the phonebook is exposed, access may expand beyond the individual device to an entire organization, family, or business network.
This feature functions as a network-intelligence tool, enabling analysis of the target's social graph, hierarchy of relationships, and points of influence.
Operational Capabilities
Messengers / Notification Monitoring Page
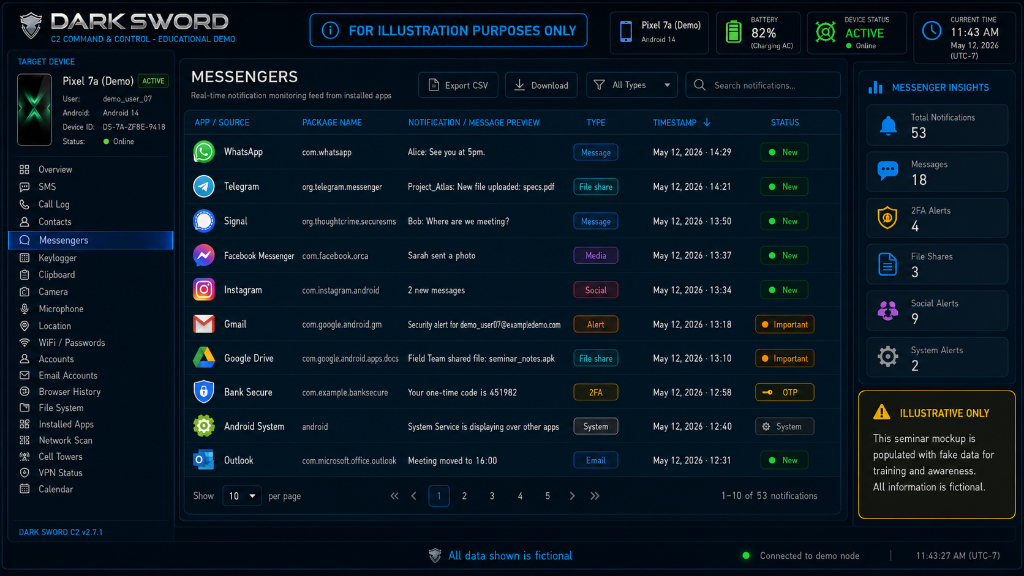
The messenger module monitors notifications from WhatsApp, Signal, Telegram, Facebook Messenger, Gmail, Google Drive, and other applications — displaying package names, notification text, message previews, timestamps, file-sharing alerts, system notifications, and push alerts.
Security Significance
Even where full encrypted chat extraction is not possible, notification content may still reveal message previews, OTP codes, sender names, banking alerts, and sensitive context.
This module provides real-time visibility into communications, capture of notification-based verification codes, monitoring of file-sharing activity, and privacy compromise across multiple apps simultaneously.
Operational Capabilities
Keylogger Page
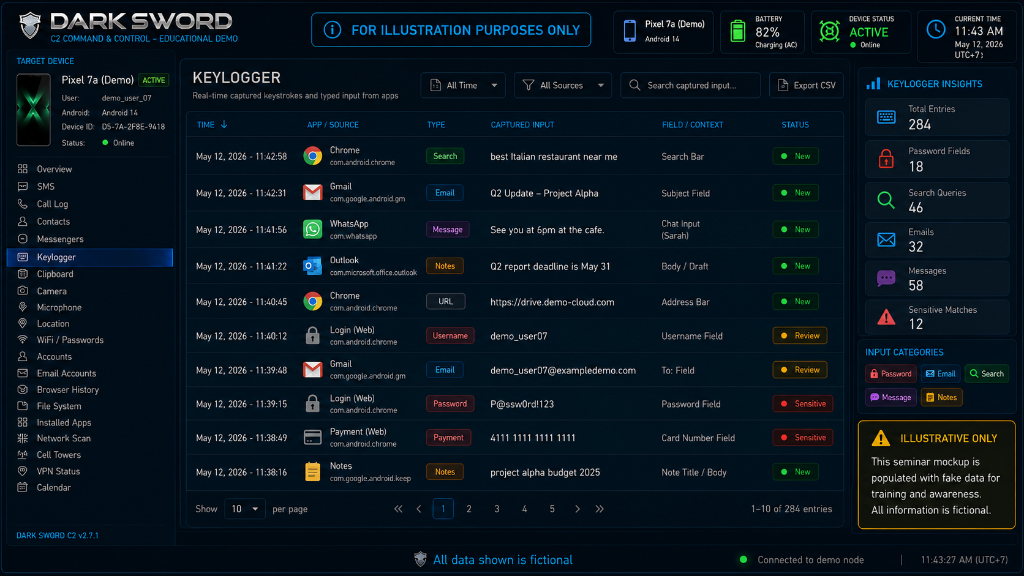
The keylogger module records typed input across apps — capturing passwords, login details, search queries, emails, credit card numbers, and other text entered into the device.
Security Significance
A keylogger turns the phone into a credential-harvesting device. It can defeat many security controls because it captures secrets at the exact moment the user enters them — bypassing encryption, password managers, and two-factor authentication alike.
This module enables monitoring of potential theft of passwords, banking credentials, crypto wallet data, business logins, private messages, search queries, and personal information.
Captured Data Categories
Clipboard Monitoring Page
The clipboard module reads copied content and may also replace it. It captures passwords, links, crypto addresses, OTP codes, bank details, IBANs, credit card data, private messages, and copied images or text.
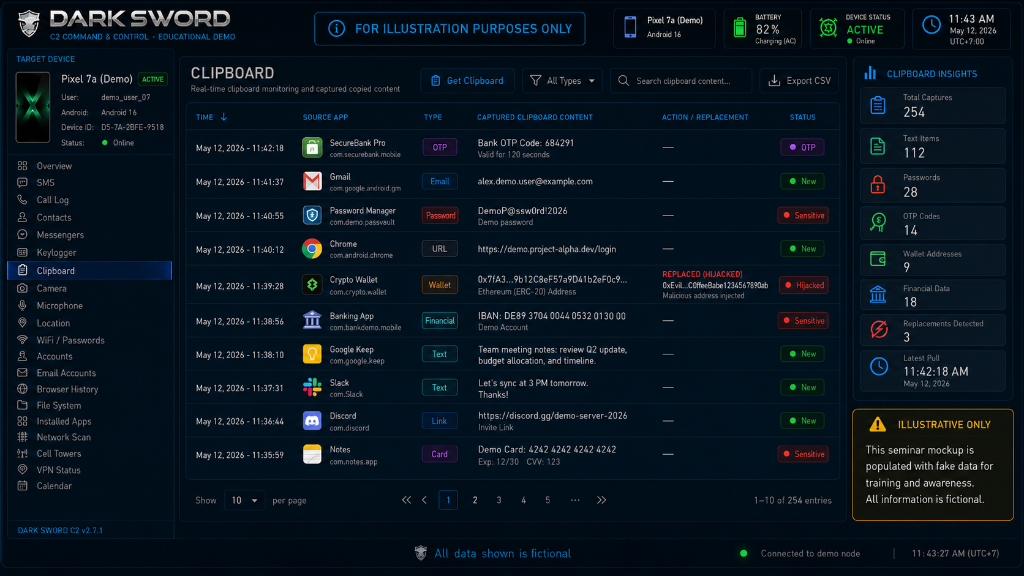
Security Significance
The clipboard is often used as a temporary bridge between apps. Users copy passwords, crypto addresses, bank details, verification codes, and private content without realizing that the clipboard can be monitored — or actively manipulated.
This module enables monitoring of credential theft, OTP theft, crypto address replacement, payment redirection, data manipulation, and account compromise — all triggered silently by a simple copy action.
Risk Categories
Camera Page
The camera module allows remote use of the front camera, rear camera, or both — taking photos, starting or stopping video recording, uploading captured media to the dashboard, previewing content, and downloading files.
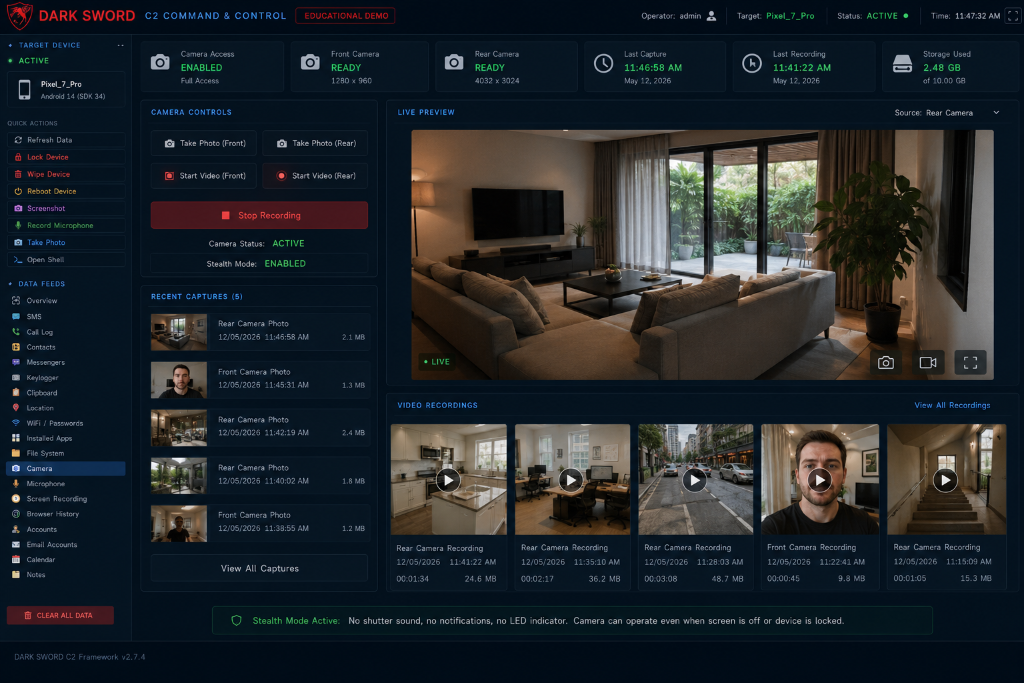
Security Significance
Camera access converts the smartphone into a visual surveillance sensor — enabling capture of sensitive documents, observation of people nearby, exposure of the user's home or office, and collection of compromising images or videos.
This feature illustrates the physical-world connection: the device is not only a data container — it is also a camera, microphone, GPS tracker, and network sensor operating silently in the target's environment.
Surveillance Capabilities
Real Time Screen Video Page
The screen video module lets the operator trigger a real-time recording of the target phone's screen from the dashboard — seeing remotely exactly what the user sees on the device, as it happens, and then playing back or downloading the captured screen video at any time.
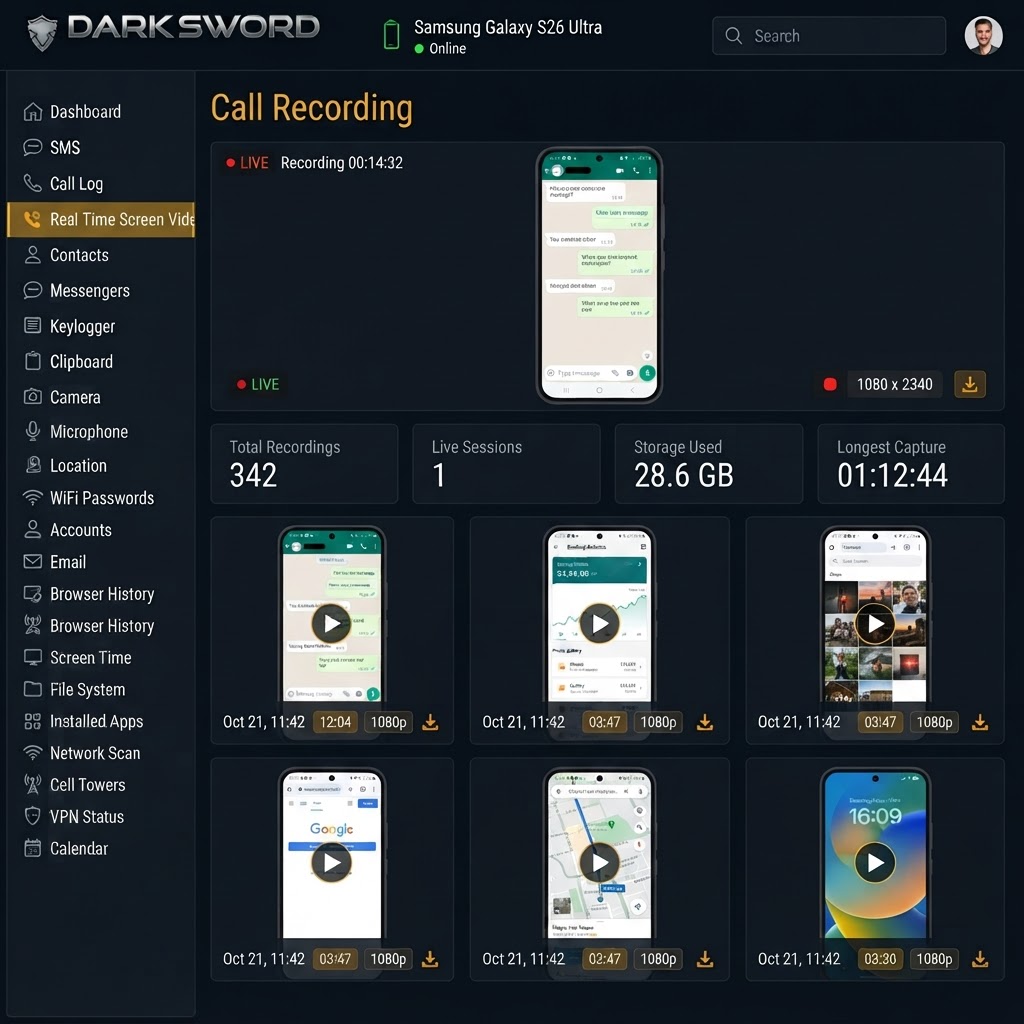
Security Significance
Screen video bypasses application encryption entirely. Because the content is captured after it has been decrypted for display, the operator sees messages as they are read and written, passwords and one-time codes as they are entered, banking balances, photo galleries, contacts, and every other screen the user opens — including apps that offer no other monitoring path.
A recording starts on command from the dashboard and continues for as long as the session runs. Each capture is stored as a timestamped video entry with its duration and resolution, ready for playback or download from the same page.
Screen Video Capabilities
Sessions are collected in a library of screen recordings, each shown as a thumbnail of the captured screen with its timestamp, duration, and resolution, alongside a live view of the device mirroring the current screen in real time.
Microphone Page
The microphone module supports remote audio recording, including room audio and possibly voice-call audio. The dashboard displays date/time, duration, file size, filename, audio preview, and download options such as MP3 or MP4.
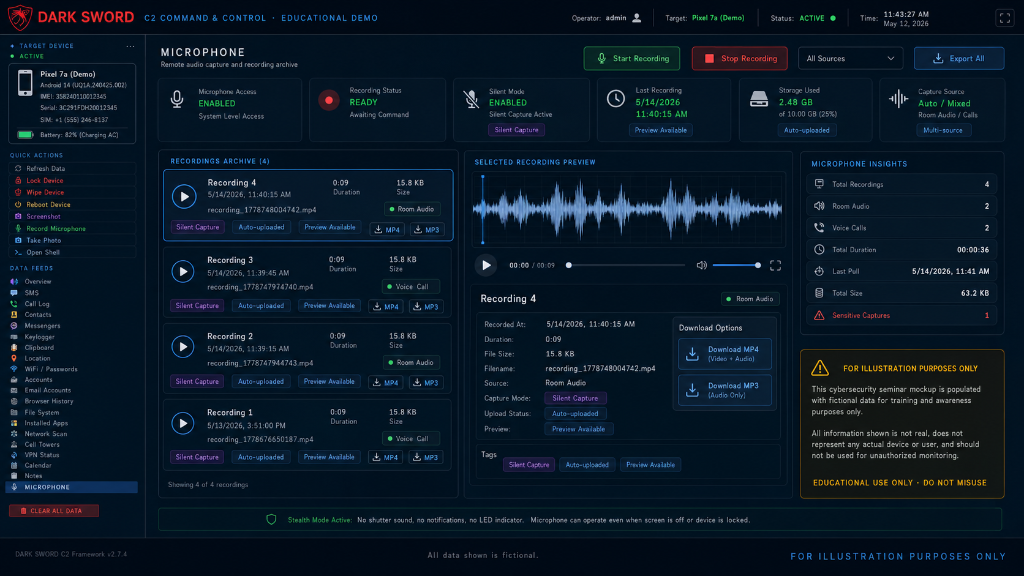
Security Significance
Microphone access enables covert collection of conversations near the phone — exposing meetings, private conversations, business negotiations, legal discussions, medical conversations, family conversations, and calls.
For executive, government, legal, and corporate environments, microphone compromise is one of the most serious capabilities — the phone becomes a live intelligence-collection device operating silently inside any room.
High-Risk Environments
Location / GPS Page
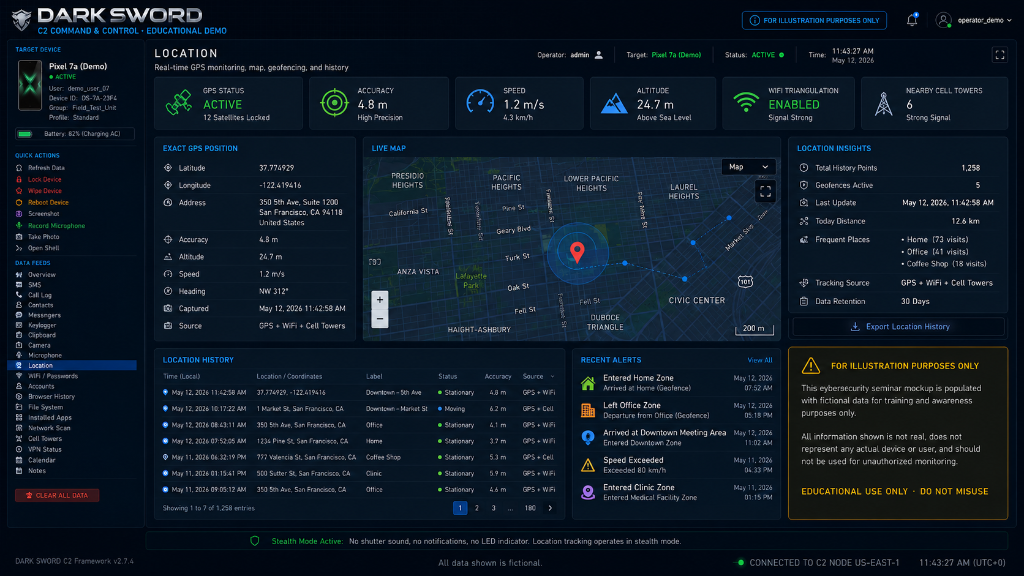
The location module displays latitude, longitude, address, accuracy, altitude, speed, map view, and location history — including live updates, historical tracking, and geofencing-style alerts.
Security Significance
Location tracking connects digital compromise to physical surveillance — enabling stalking, exposure of home and work addresses, identification of routines, tracking of family locations, monitoring of travel, and timing of physical or cyber operations.
Location data is not just a map coordinate. Over time, it becomes a behavioral profile: where the person sleeps, works, meets others, travels, and spends private time.
Intelligence Value
WiFi / Passwords Page
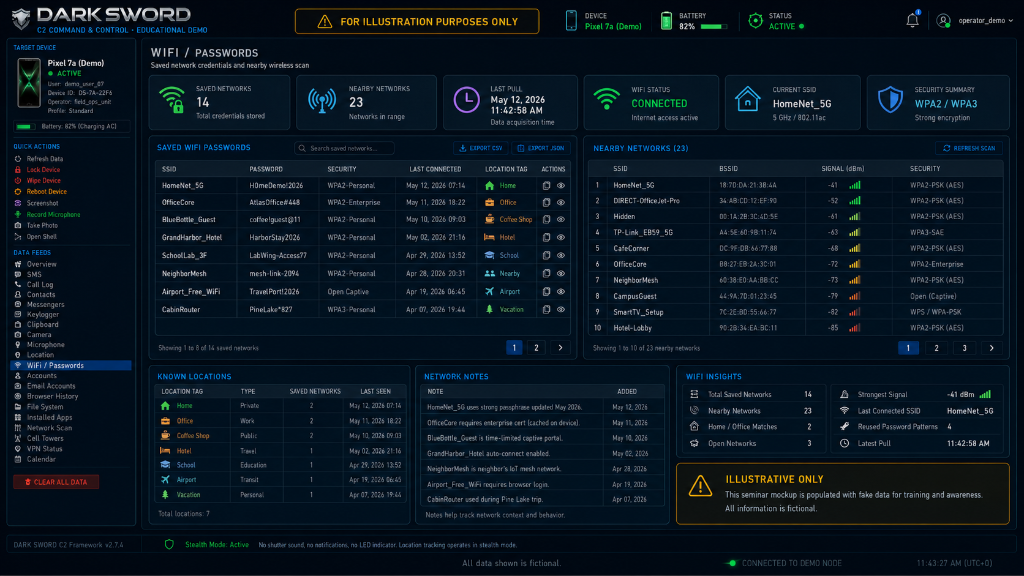
The WiFi module lists saved WiFi networks and may expose WiFi passwords. It also shows nearby networks with SSID, BSSID, signal strength, and security type.
Security Significance
WiFi data connects the phone to the user's physical locations and networks. Saved WiFi names may reveal home, office, hotels, airports, schools, and other places the user has visited.
This includes exposure of home or office network credentials, mapping of user movement, possible lateral movement into local networks, and password-reuse attacks against other accounts and services.
Attack Vectors
Accounts Page
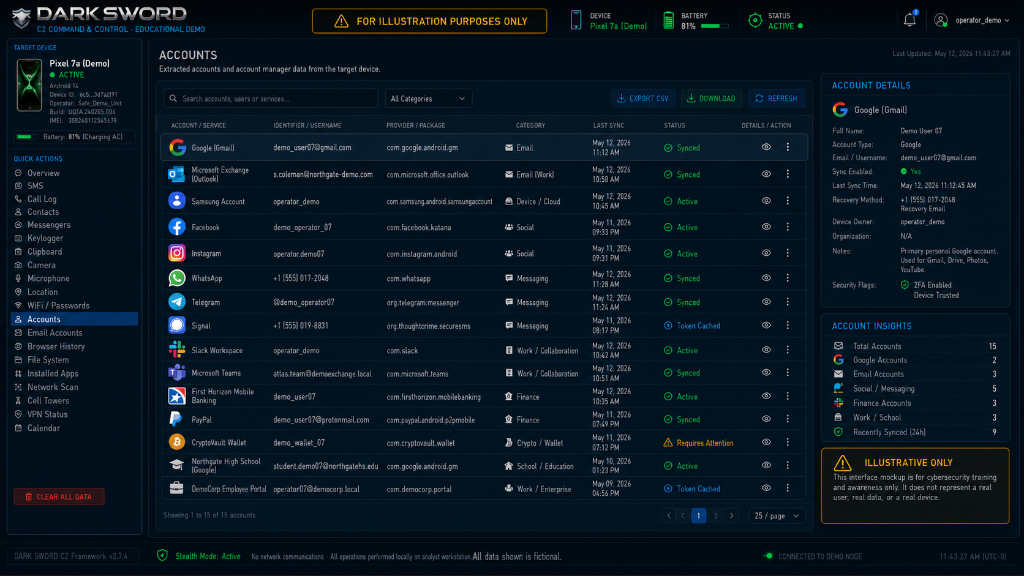
The accounts module lists accounts configured on the Android device — including Google/Gmail, Outlook, Yahoo, corporate Exchange, manufacturer accounts, social media, messaging apps, work accounts, school accounts, banking/finance apps, and other apps integrated with Android account management.
Security Significance
Even without passwords, knowing which accounts exist on a device is valuable intelligence. It allows attackers to tailor phishing messages and account-recovery attacks with precise targeting.
This module enables targeted phishing, password reset attacks, account takeover attempts, impersonation, and identity mapping — all derived from a simple list of registered accounts.
Operational Capabilities
Email Accounts Page
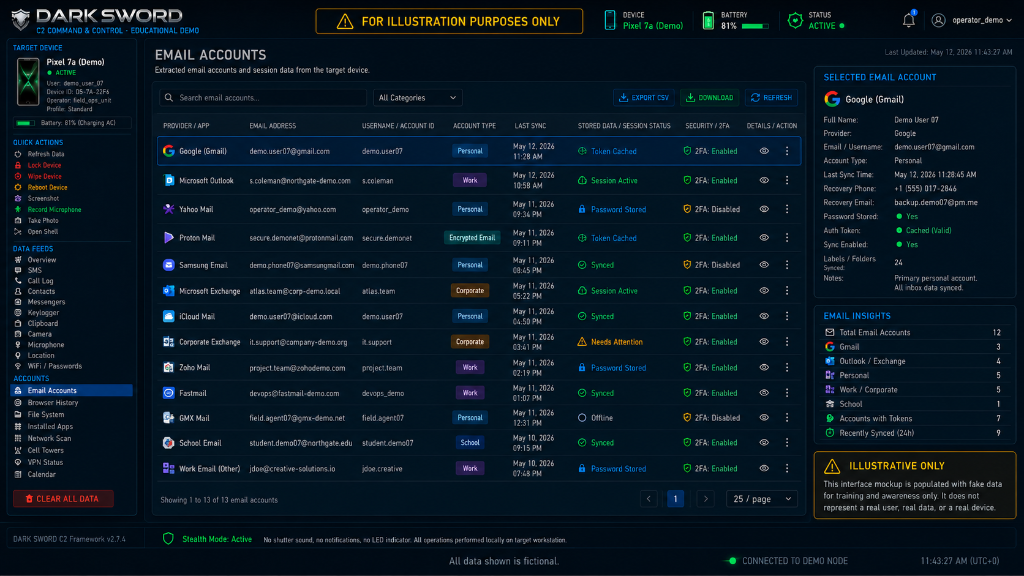
The email accounts module displays configured email addresses, provider type, username, last sync time, and possibly authentication-related data if accessible.
Security Significance
Email accounts are often the central recovery mechanism for banking, social media, cloud storage, crypto exchanges, business platforms, and identity services.
Email compromise can become a master key. Once email is compromised, many other services can be reset or accessed — enabling takeover of linked accounts, business email compromise, exposure of corporate communications, and identity fraud.
Attack Vectors
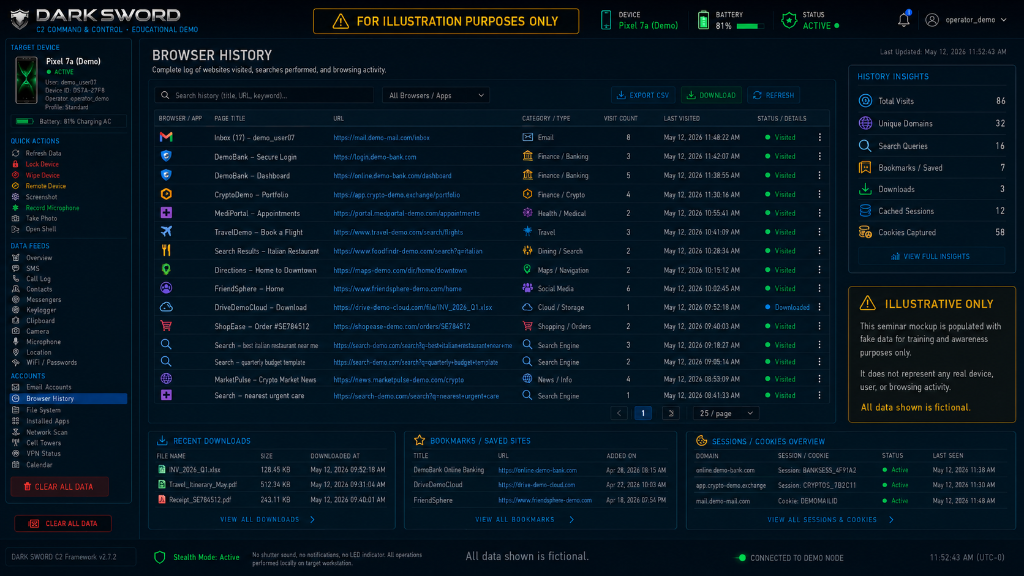
Browser History Page
The browser history module displays visited websites, page titles, timestamps, visit counts, search queries, downloads, bookmarks, cookies, cached sessions, form data, and other browser artifacts.
Security Significance
Browser data reveals interests, intentions, sensitive services, financial activity, medical searches, private behavior, and possible logged-in sessions — including profiling, blackmail leverage, and identification of crypto or banking platforms.
Browser artifacts can reveal both technical and personal intelligence. They help attackers understand what the user values, fears, uses, and trusts — turning browsing history into an actionable intelligence dossier.
Intelligence Value
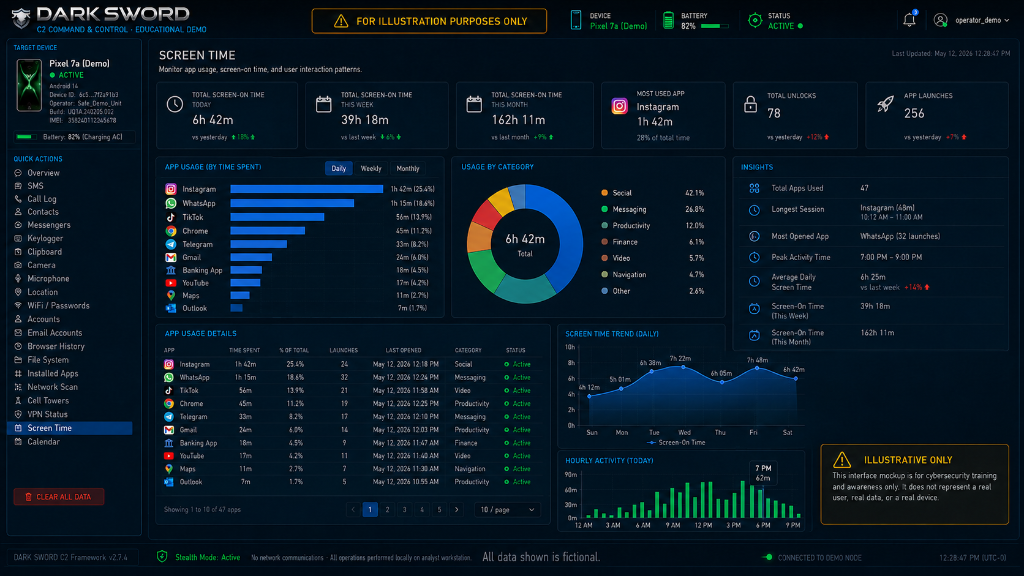
Screen Time / App Usage Page
The screen time module displays total screen-on time, app usage duration, number of app launches, daily/weekly/monthly charts, and a list of apps opened by the user.
Security Significance
App usage data creates a detailed behavioral profile of the user — revealing which banking apps, crypto wallets, dating apps, work tools, password managers, and 2FA apps they rely on daily.
Knowing which apps a user opens most often helps an attacker choose the best social-engineering theme or timing — turning screen time data into a precision targeting tool for phishing, impersonation, and account takeover.
Profiling Capabilities
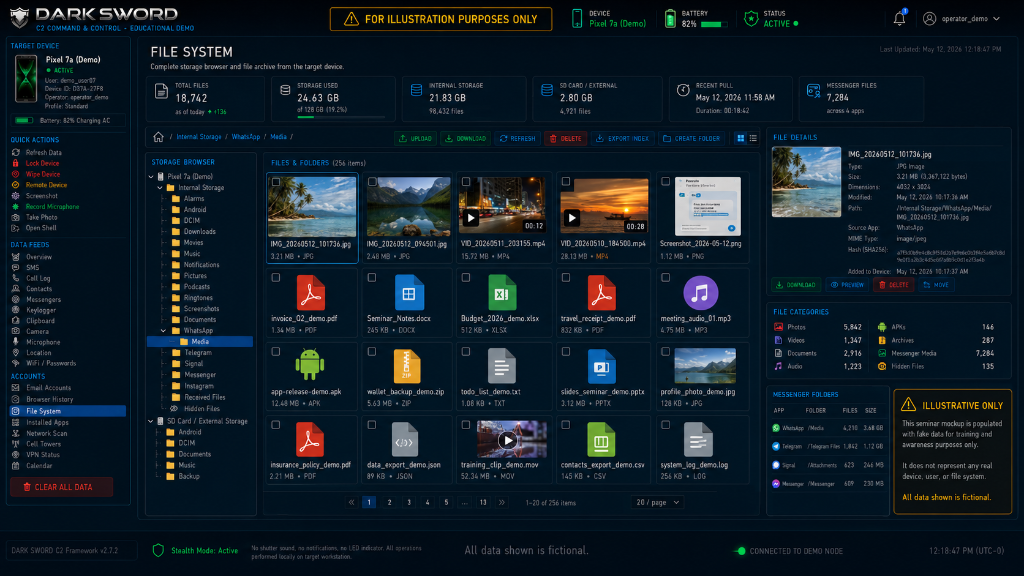
File System Page
The file system module provides access to device storage — displaying photos, videos, audio recordings, documents, downloads, screenshots, APK files, hidden files, system files, and messenger media folders such as WhatsApp, Telegram, Signal, Facebook Messenger, and Instagram.
Security Significance
File access is one of the most powerful capabilities — exposing private media, business files, identity documents, contracts, invoices, wallet files, and received attachments. It enables data theft, extortion, intellectual property theft, and tampering with files remotely.
This module represents the difference between "monitoring" and full remote data control — giving operators the ability to browse, download, and interact with the entire device storage as if physically holding the device.
Operational Capabilities
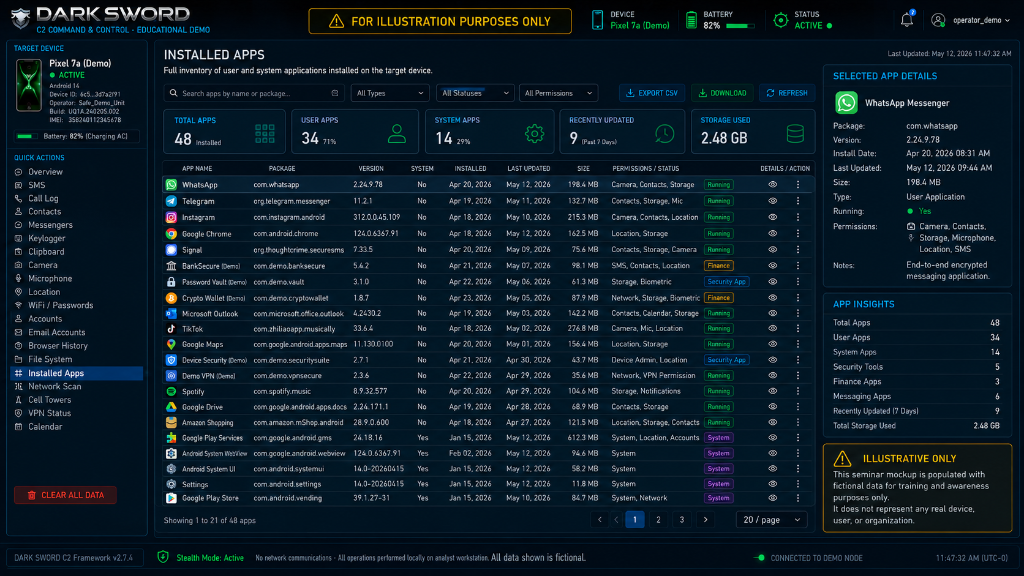
Installed Apps Page
The installed apps module lists user-installed and system apps — including app name, package name, version, install date, last update date, app size, permissions, and running status.
Security Significance
Installed app inventory provides reconnaissance about the user's habits, financial services, security tools, work platforms, and possible defensive software — enabling target selection, security evasion, and tailored phishing campaigns.
An app list is a personal and professional fingerprint. It reveals what kind of person or organization the device belongs to and which attack path may be most effective — from banking apps and crypto wallets to 2FA authenticators and corporate tools.
Intelligence Value
Network Scan Page
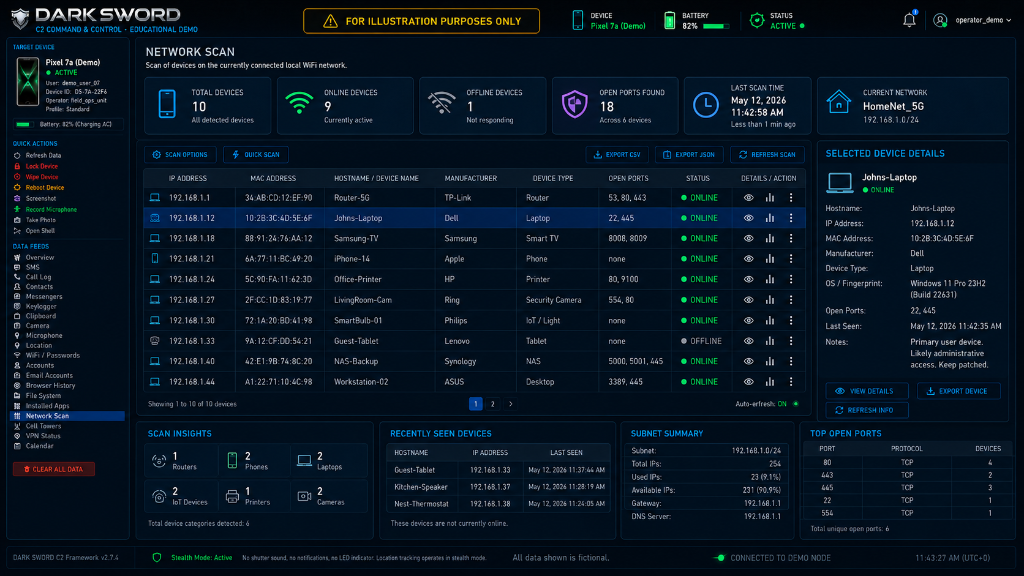
The network scan module scans the local WiFi network to which the phone is connected — displaying IP addresses, MAC addresses, hostnames, manufacturers, device types, online/offline status, and open ports.
Security Significance
The phone becomes a reconnaissance point inside the local network — enabling mapping of home or office devices, identification of laptops, smart TVs, cameras, printers, routers, and IoT devices, and preparation for lateral movement attacks.
The mobile phone should not be treated as isolated — it can become a bridge into the internal network environment, exposing infrastructure that is otherwise air-gapped from the internet.
Operational Capabilities
Cell Towers Page
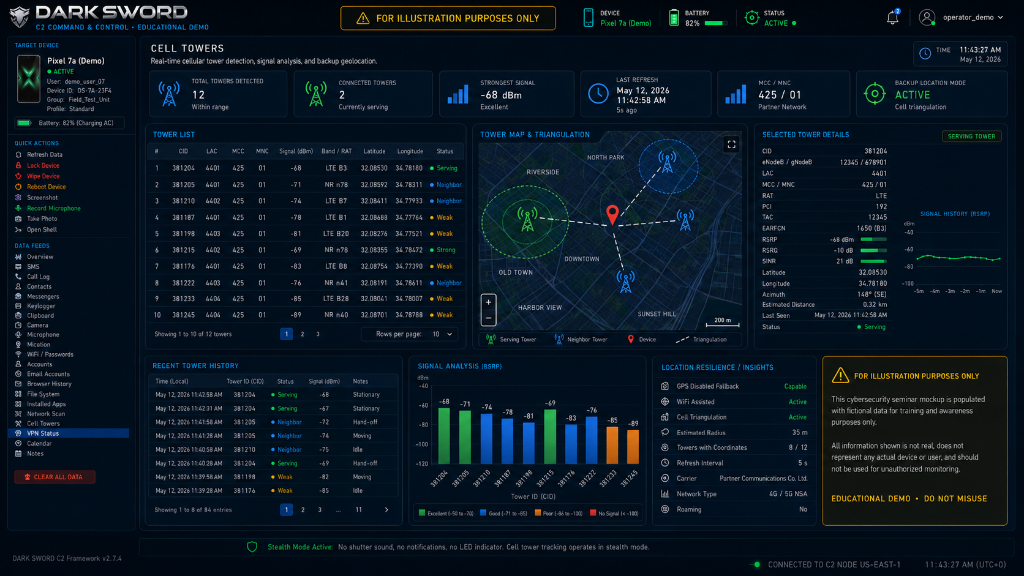
The cell towers module displays nearby and connected cellular towers — including Cell ID, Location Area Code, Mobile Country Code, Mobile Network Code, signal strength, tower coordinates, real-time updates, and a map display.
Security Significance
Cell tower data supports location tracking even where GPS is weak, unavailable, disabled, or unreliable — providing backup geolocation, movement analysis, and correlation with other signals.
Location tracking is strongest when multiple signals are combined: GPS, WiFi, cell tower metadata, IP address, and movement speed. Together they form a near-continuous, high-confidence position record.
Operational Capabilities
VPN Status Page
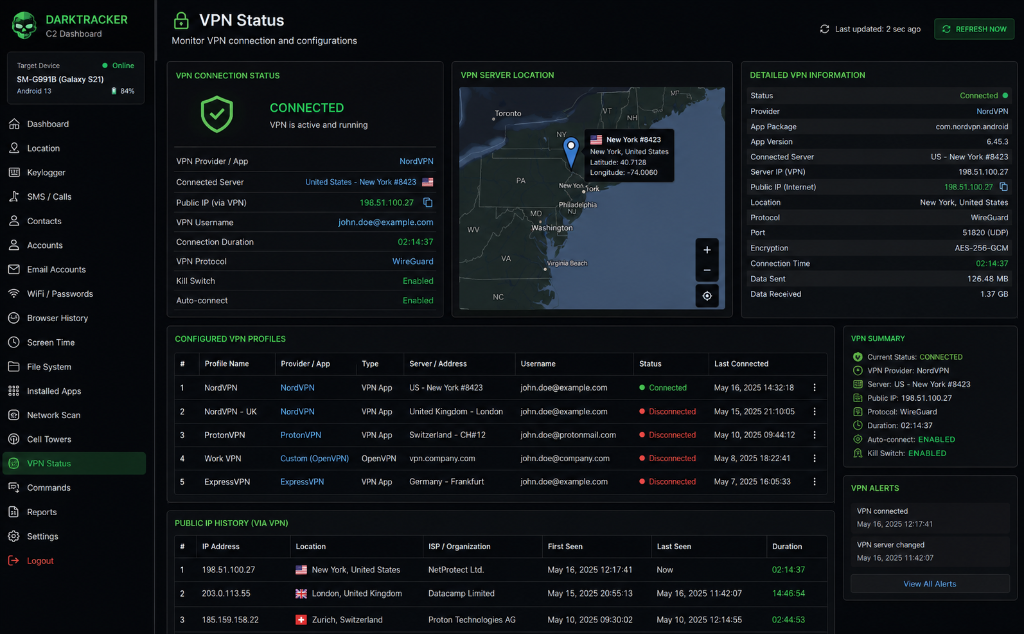
The VPN module displays connection status, provider or app name, connected server, public IP address, username, connection duration, VPN protocol, and all configured VPN profiles on the device.
Security Significance
VPN information reveals whether the user is attempting to mask their network location or route traffic through a privacy service — exposing the VPN provider, server location, public IP, account credentials, and configuration for potential targeting.
VPNs protect network traffic in transit, but endpoint compromise can still expose local data, credentials, screenshots, keystrokes, and sensor output — rendering the VPN's privacy guarantees irrelevant.
Operational Capabilities
Calendar Page
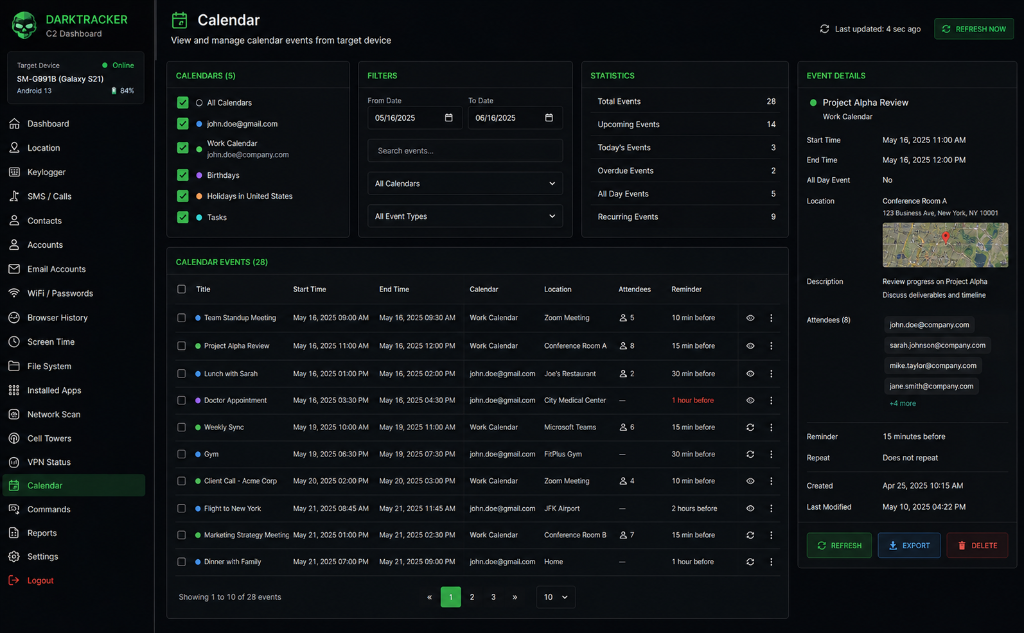
The calendar module extracts events from Google Calendar, Samsung Calendar, Outlook, Exchange, and other synced calendars — including title, date, start and end time, location, description, notes, attendees, recurring events, and reminders.
Security Significance
Calendar access exposes the user's full schedule — meetings, travel, appointments, deadlines, and personal or professional commitments. This enables physical stalking, timed phishing attacks, business intelligence gathering, and targeted intrusion planning.
Calendar data is operational intelligence. It tells an attacker where the person will be, when they are busy, who they are meeting, and what topics may be sensitive — making it one of the most strategically valuable data sources on a device.
Operational Capabilities
C2 Data Flow Schematic
Illustrative architecture only — no live data, device identifiers, or operational details are shown. This diagram depicts how intelligence moves from the hardware implant to the operator's C2 dashboard over a protected channel.
Target Device
Samsung Galaxy flagship
Looks & behaves as a normal smartphone to the user.
Hardware Implant
Beneath the Android OS
Dedicated chipset — no OS process, file, or socket.
Encrypted Channel
Out-of-band transport
Hardware-bound session keys; mutual authentication.
C2 Dashboard
Operator interface
20 capabilities on one authenticated session.
Diagram is a sanitized representation. Actual C2 interfaces, device identifiers, and operational telemetry are withheld for operator and client security.
Operational Assurance
Five guarantees that hold inside a live operation
A monitoring platform is judged in the field, not in a specification. These are the five commitments the platform is built around — each one enforced in the delivered product, and each one inspectable in the source code your agency receives.
Each guarantee is delivered in the product and open to inspection in the source code, so your agency verifies the commitment rather than accepting it.
Lawful undercover operational support
Authority is established before the first device is enrolled, and the platform keeps the record that proves the operation stayed inside it.
- Enrollment tied to a named operation and its authorization reference
- Named officers hold the authority to task, collect and export
- Per-operation audit trail of every command, collection event and export
- Support engineers work only through documented, logged channels
Agent safety
The operative's cover is the most fragile asset in the operation, so protection never depends on picking the handset up.
- Discreet remote check-in and duress alerts straight to the handler
- Live location held by command during meetings, handovers and stops
- Camera, microphone and screen access without touching the device
- Immediate session revocation and evidence preservation if it is seized
Secure communications
Handler tasking and collected material travel out of band, on a hardened channel that never enters the device's ordinary messaging.
- Mutual authentication with hardware-bound session keys in both directions
- Tasking recorded in the agency audit trail, not a commercial chat log
- Quantum-resistant CryptShield encryption over intelligence and evidence
- No third-party cloud anywhere in the path of operational traffic
Mission continuity
An operation cannot pause for a rebuild. Collection survives reboots, connectivity loss and attempts to remove the application.
- Collection resumes automatically after restart or factory reset
- Local buffering through network blackouts, synchronized on reconnection
- Operation handover between handlers and shifts without losing context
- Source ownership lets your agency maintain and rebuild without a vendor
Evidence integrity
An exhibit is only worth what can be proven about it, so every item is anchored at capture and preserved with the record of every hand it passed through.
- Device-side capture timestamps preserved through the whole pipeline
- Cryptographic hash on arrival, matched against the file used in the case
- Original items retained beside every transcript, excerpt and export
- Access and export registers showing who viewed or took the material
One-time technology acquisition, permanent operating rights
Unlike vendors that retain control over their proprietary software and require continuous subscription payments, we deliver the complete technology — source code, technical blueprints, engineering documentation and know-how transfer.
- Complete source code of the Android agent application and the C2 dashboard
- Technical blueprints and engineering documentation
- Full know-how transfer to your technical teams
- Installation on your own servers and secure infrastructure
- Independent inspection and audit of the entire delivered source code
- Exclusive operational control over your intelligence data and enrolled devices
- Independent operation, maintenance and further development
- Technical support, installation assistance and operator training
- No dependence on external cloud infrastructure
- No mandatory recurring software licensing
- Non-exclusive acquisition — the technology becomes yours to run
Acquisition is subject to lawful-authority verification and a signed mutual non-disclosure agreement.
Absolute control over your data, with no one left to depend on
A one-time acquisition with the complete source code changes what your agency actually owns. The platform stops being a service you are granted access to and becomes an asset held inside your own perimeter — with no vendor standing between you and your intelligence.
In practice
No subscription expiry. No seat counts. No vendor permission required to keep operating the platform you acquired.
Data that never leaves your perimeter
Collected intelligence is stored on servers your agency operates. No vendor cloud, no shared tenancy, and no third party that could be asked for your case material.
No telemetry, no call-home
The delivered build reports nothing back to us: no license check, no usage telemetry, no remote kill switch. What happens inside your network stays inside it.
Keys generated and held by you
Device and data encryption keys are created in your environment and never leave your custody, so no one outside your agency can decrypt operational material.
Keep it, audit it, fork it, extend it
Your engineers receive the full source, blueprints and documentation. Modify it, rebuild it, integrate it with your own systems, or continue development entirely in-house.
Technology you own, not a subscription you rent
Most surveillance platforms keep the software, the infrastructure and your intelligence data under vendor control. Our acquisition model delivers the platform itself.
Full capability comparisonPractical implications for agencies
Long-term cost control
Attractive for agencies that expect multi-year or permanent use, because the cost is front-loaded rather than perpetual.
Operational security
Ability to run the system without continuous external connectivity or vendor oversight reduces exposure.
Strategic independence
Especially relevant for national intelligence or high-sensitivity units that prefer not to depend on a foreign or commercial SaaS provider.
Customization for specific tradecraft
Agencies can adapt the Android client and C2 to their exact operational procedures, legal constraints or integration needs — something harder with closed platforms.
Auditable code, not a black box
Assurance that a platform is secure has to be verifiable rather than promised. Because the source is delivered, your team — or an independent firm you appoint — can inspect the exact code that will run your operations, line by line, before it is deployed.
Line-by-line inspection before acceptance
Every module of the Android agent application and the C2 dashboard is delivered as readable source. Your security team reviews authorization logic, cryptography and data handling before sign-off.
No hidden access paths
No undocumented accounts, no maintenance backdoor, no covert channel back to the supplier. Every external interface is declared in the documentation and can be disabled by your administrators.
Dependency transparency
The full inventory of third-party libraries, versions and licenses ships with the delivery, so nothing enters your environment unexamined or unattributable.
Cryptography you can verify
Key generation, rotation and storage are implemented in the delivered code with documented algorithms, so the encryption protecting intelligence can be tested rather than trusted.
Vulnerability handling that keeps working
Security findings are triaged by severity, corrected in the codebase and delivered as patches with a written description of the flaw and the change.
Re-audit whenever you choose
With the code in your hands, a fresh review needs no vendor approval and no escrow release — commission one before a sensitive deployment or after any change you make.
Supported for the life of the platform you own
Ownership without support becomes a burden. The acquisition includes a long-term engineering relationship alongside the code: installation, training, maintenance and a defined path for every security update — while the platform itself stays under your control.
Engineering support that knows the codebase
- Named engineering contacts for the duration of the support term
- Installation, integration and hardening assistance in your own environment
- Incident response and root-cause analysis for operational faults
- Operator and administrator training, with written runbooks and documentation
Updates on your schedule, never forced
- Security patches prioritized, each delivered with the flaw and the fix described
- Feature development coordinated with your change-control and deployment windows
- No forced upgrades, no remote disabling, no end-of-life switch that stops the platform
- Your team can apply, adapt or author patches independently — the source is already yours
Liability & warranty at a glance
Warranty
The delivered build conforms to the technical specification for an agreed warranty period after acceptance.
Defects
Confirmed defects are remediated by our engineering team at no additional cost during the warranty term.
Liability
Defined in the signed acquisition agreement, with agreed caps, exclusions for unlawful use and a documented claims process.
Confidentiality
Mutual NDA covering the engagement, the delivered code and every operational detail shared during evaluation.
Governing terms
Jurisdiction, dispute resolution and support duration are fixed in writing before delivery, not changed unilaterally afterwards.
Source escrow
Not required. The complete source code is handed over outright, so there is no escrow release to depend on.
Support term, warranty period and liability terms are set out in the acquisition agreement signed by both parties.
Evaluate the platform on your own test devices
We invite your organization to a confidential technical presentation and a 7-day evaluation of the existing Android application and centralized C2 dashboard, using authorized test smartphones.
- 1Confidential technical presentation for your authorized unit
- 27-day evaluation on test Android smartphones you nominate
- 3Debrief with your technical and operational teams
Additional secure communications, encryption and AI integrations can be demonstrated or discussed according to their implementation status and your operational requirements.
Governance & Assurance
Assurance built into the acquisition
Agency Data Sovereignty
All intelligence remains on infrastructure your agency controls.
Source Code Custody
Delivered code, blueprints and documentation held by your organization.
Quantum-Resistant Encryption
CryptShield protects intelligence files and digital evidence.
Cyber-Link Secure Comms
Hardened encrypted channel between operatives and command.
Mutual NDA & Vetting
Every engagement begins with confidentiality and lawful-authority verification.
Support & Training
Installation assistance, technical support and operator training included.
Authorized government and law-enforcement deployment only
This platform is provided exclusively to government intelligence agencies, police departments and law enforcement organizations for the authorized monitoring, protection and coordination of undercover operatives, infiltrated agents and field intelligence personnel. Every deployment requires a documented lawful mandate within the acquiring jurisdiction.
Authorized Buyers
Only vetted government intelligence agencies, police departments and law-enforcement organizations with a documented lawful mandate may acquire or operate the platform.
Operational Responsibility
The acquiring agency is solely responsible for the lawfulness of each operation, for the authorization covering every enrolled device, and for the internal oversight of its operators.
Prohibited Use
Use against persons outside an authorized investigation, political or religious surveillance, or any deployment without lawful authority is strictly forbidden and voids all rights of use.
Acquisition and deployment are conditional upon lawful-authority verification and acceptance of our legal notice.
Agency deployment under a documented lawful mandate
This platform is provided exclusively to government intelligence agencies, police departments and law enforcement organizations for the authorized monitoring, protection and coordination of their undercover operatives. Every operation requires lawful authority within the acquiring jurisdiction, and the acquiring agency remains responsible for the authorization covering each enrolled device. We do not provide the platform for unauthorized surveillance, stalking, or use outside a lawful investigation. Each request is reviewed before any acquisition, and all deliveries are conditional upon acceptance of our legal notice.